SBI data leak raises fraud risk as bank probes exposure of customer records | Today’s news
Mumbai: State Bank of India (SBI) is investigating the exposure of thousands of customer records on the dark web, with cyber security experts warning that the breach could expose affected customers to targeted fraud and social engineering attacks, even as the bank’s core systems and account balances remain secure.
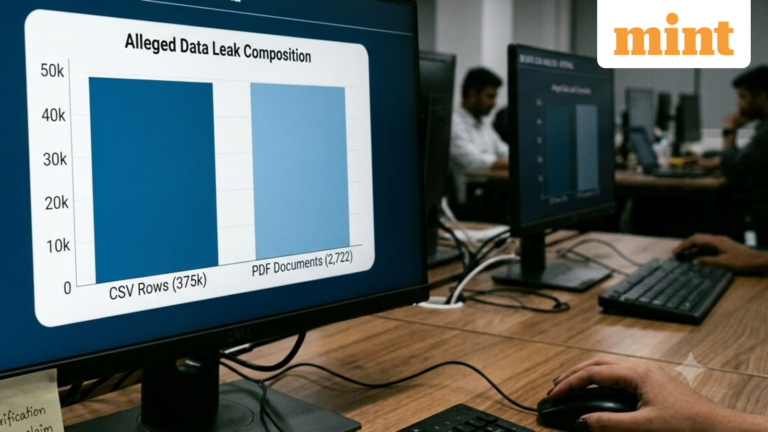
In a regulatory filing to the stock exchange on Wednesday, SBI said it received an alert on October 16 from its threat intelligence provider, the Defense Cyber Agency and the Indian Computer Emergency Response Team (CERT-In) about suspected exposure of customer data on the dark web. A preliminary analysis of approximately 375,000 records found on the dark web identified 3,897 records containing personal information, including names, registered mobile numbers, dates of birth, gender, email and residential addresses, branch and customer identifiers, lead IDs and metadata associated with loan and lead records. The SBI said it has appointed an independent cyber security agency, part of CERT, to assess the authenticity, completeness, origin and scope of the exposure.
The bank said the incident is not expected to have a significant impact on its information technology systems, core business operations, financial performance or business continuity. It also said it activated its cyber incident response and containment protocols after receiving alerts.
Read also | SBI data breach claims: Hacker allegedly leaked 3.75 million records, 2,722 PDF documents
Dhiraj Gupta, chief technology officer (CTO) and co-founder of cybersecurity firm mFilterIt, said the leaked information could provide fraudsters with enough details to make the scams more convincing.
“All this data will allow fraudsters to create a profile of you. They will be able to target you with accurate information and use it to build your trust,” Gupta said.
He warned customers not to assume the caller is real because they know personal information. “The problem is that customers have to be careful that just because someone says all this information, they can’t assume that person is genuine. This data is now out there and publicly available.”
SBI did not immediately respond to Mint’s queries.
Read also | Refund after sharing OTP? What Kerala HC ruling in SBI scam case means
The SBI incident is the second major cyber security attack on a public sector bank in recent months after Bank of Baroda disclosed a security incident in July involving unauthorized access to certain data after an employee’s email account was compromised. Bank of Baroda also said its core banking systems were not accessible.
Mint had earlier reported that the Bank of Baroda incident came to light around the lender’s June earnings and that the timing warranted scrutiny.
Gupta said such compromises can occur over extended periods of time as attackers work their way through systems. “These breaches happen over days and weeks. Someone accesses a system, finds more information, potentially finds more access points, and then moves into those systems and databases,” he said.
He also said that ransomware could be one possible reason for a security breach in such cases, while stressing that he had no information on whether this happened in the SBI incident.
Another area that investigators can look into is third-party access. “Supplier compromise is always possible. Vendors have enough access these days and that’s why RBI has mandated vendor audits. Banks are now required to audit themselves and their vendors for security,” Gupta said.
Pavan Duggal, a senior advocate of the Supreme Court and an expert in cyber law, described the incident as significant given the scale and customer base of SBI. “This is not an ordinary breach. It is a serious matter which needs to be thoroughly investigated keeping in mind the size of SBI and the number of accounts held by SBI,” he said.
Read also | Refund after sharing OTP? What Kerala HC ruling in SBI scam case means
He also pointed to RBI’s cyber security and IT governance framework under which banks can face regulatory action and monetary penalties for specific non-compliance.
Later in the day, SBI issued a new statement about X, which sought to reassure customers that the incident affected a “very, very small number of customers” and that “customer balances are completely safe.” The bank reiterated that the incident had no significant impact on its IT systems, core operations, financial performance or business continuity, and said protecting financial assets, data and customer trust remained its top priority.
However, Gupta said the consequences of exposed personal information can linger beyond the immediate incident. “What’s already gone is now the customer’s problem for the next five years. But what they can do is strengthen their security to make sure that what hasn’t gone can still be protected.”
“Should this data breach occur after the DPDP Act 2023 comes into full force from 13 May 2027, the bank will be liable to pay fines of ₹250 crore for the violation, payable to the Consolidated Fund of India,” Duggal said.