How does India deal with service outages?
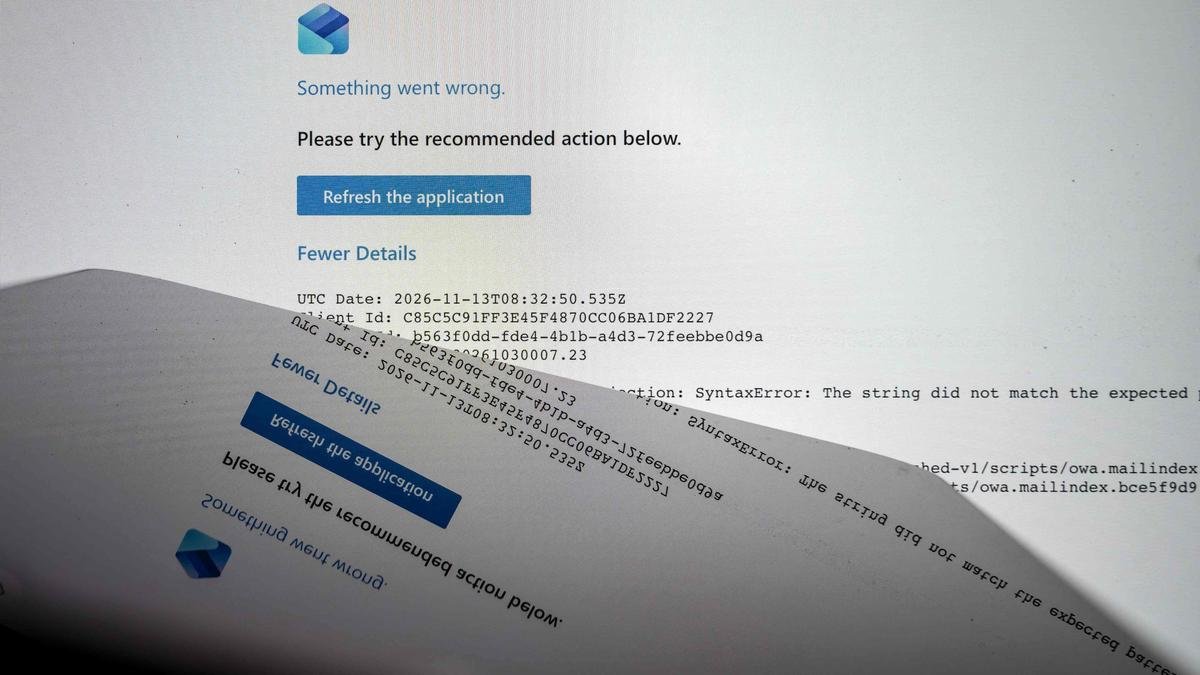
From November 12 to 13, an as yet unspecified problem with Microsoft’s infrastructure affected the ability of customers to access its Microsoft 365 productivity suite worldwide, including its Outlook email service. Microsoft apologized during the outage, blaming the incident on a failure to upgrade its network capacity, although more precise details are still awaited.
In India, in addition to ramifications across sectors, IndiGo and Akasa Air have alerted passengers to the suspension of their email support, while Air India has redirected its email.
The incident raises further questions about whether service companies that thousands of people depend on should be held accountable for such failures in India.
Does Indian law require Microsoft to report an outage?
There are three sets of rules and each has a loophole.
First, the guidelines issued by India’s Computer Emergency Response Team (CERT-In) on April 28, 2022 under the Information Technology Act, 2000 require companies to report cyber incidents within six hours. The guidelines cover attacks and intrusions, but not outages caused by technical faults. However, CERT-In may request information under Section 70B(6) of the IT Act and seek clarification from Microsoft.
The second is the Reserve Bank of India’s Outsourcing Risk Management Guidelines, issued on 28 November 2025. They carry forward the rules for outsourced IT services, which first came into force on 1 October 2023. A bank purchasing cloud services must assess its reliance on the vendor and have an exit strategy. If the arrangement fails, the RBI can hold the bank responsible and the bank can seek an explanation from Microsoft under its contract.
The third is the Personal Data Protection Act of 2023. The Act defines a personal data breach to include an accidental “loss of access to personal data”. Under the rules, which are due to come into force in May 2027, a breach of personal data must be reported to the Privacy Council and to each affected person. Failure to report can result in a fine of up to ₹200 million. The onus is on the organization that collected the data, and that organization is a Microsoft customer, even if the data resides on Microsoft’s servers.
While Indian law does not require a minimum damage threshold for reporting a breach, it is unclear whether a temporary outage constitutes a “loss of access” and thus a breach. If so, the company must report the outage; if not, the company does not have to report, even if customers complained during the day. European regulators count even a temporary loss of access as a reportable breach, but only require reporting if people are at risk.
How is it different from the July 2024 blackout?
A flawed update to Falcon Sensor, a security program sold by CrowdStrike, crashed around 8.5 million Windows computers worldwide on July 19, 2024. The machines displayed a blue error screen, known as the “Blue Screen of Death”, and kept crashing until the faulty file was removed. IndiGo canceled 283 flights. Computers didn’t crash this week because the failure occurred in Microsoft’s own data centers.
Following the incident, CERT-In issued a “critical” advisory and Union Minister for Electronics and Information Technology Ashwini Vaishnaw said his ministry was in touch with Microsoft.
How accountable are cloud companies in countries?
The European Union and the United Kingdom have placed the largest technology suppliers directly under the supervision of financial regulators. EU financial supervisors have named 19 such companies as part of their Digital Operational Resilience Act of 18 November 2025, which includes Microsoft and Tata Consultancy Services. The Indian company is already reporting to the European supervisory authorities.
From 13 July 2026, the United Kingdom placed Microsoft and three other companies under the Bank of England.
Both programs only cover services sold to financial companies.
Europe has a broader law called NIS2 that covers cloud companies across all sectors. Under the October 2024 rules, a cloud service will suffer a “significant incident” if it is completely unavailable for more than 30 minutes. A partial failure is also counted if it lasts for more than an hour and affects more than 5% or more than 1 million users of the service in the EU, whichever is less. The company should inform the national authority within 24 hours and provide a detailed notification within 72 hours.
Here is a threshold for how long the service has been down so Microsoft’s outage would count.
On October 7, Singapore passed the Digital Infrastructure Act. It requires large data centers and cloud firms to be licensed and report any service disruptions to the regulator. South Korea acted after a data center fire knocked out the KakaoTalk app in October 2022. From July 2023, large platforms and data centers there are required to submit disaster management plans to the government.
In each of these countries, the reporting obligation depends on the length of the outage and the number of affected people. According to CERT-In guidelines in India, it depends on whether there is an attack.
What are the options for Indian customers?
The customer’s claim is based on their agreement with Microsoft. If the service level is not met, the customer may be entitled to a credit, which is a discount from a future bill.
There are four routes open to India. First, CERT-In could add major service disruptions, regardless of cause, to the incidents to be reported to it. Second, the government could also subject the largest digital service providers to a direct regulator. Third, the Data Protection Board could clarify whether outages are breaches and who should report them by May 2027.
Fourth, authorities could outsource such services to Indian vendors. In December 2025, the Union government told the Lok Sabha that 12.68 lakh official email accounts had moved to a platform operated by Chennai-based Zoho. This means less dependence on foreign companies. However, if a technical fault were to bring down an Indian supplier’s email service, that company would not be required to report it to CERT-In.
Whichever path India chooses, a clear rule on who and to whom must report a major outage would serve both foreign and Indian service users.
(NV Geetha is a former senior technical director at the National Information Centre. She writes about technology and data-driven storytelling.)
Published – 17 Nov 2026 07:30 IST